One sentence answer: No ID, No Waiting No Risk. Go For The Option That Allows You To Pay Directly & Get Instant Access For Online Hosting Purchase Purposes.
You order a VPS. $5 a month, maybe ten. Card goes through, money leaves your account, you get the confirmation email.
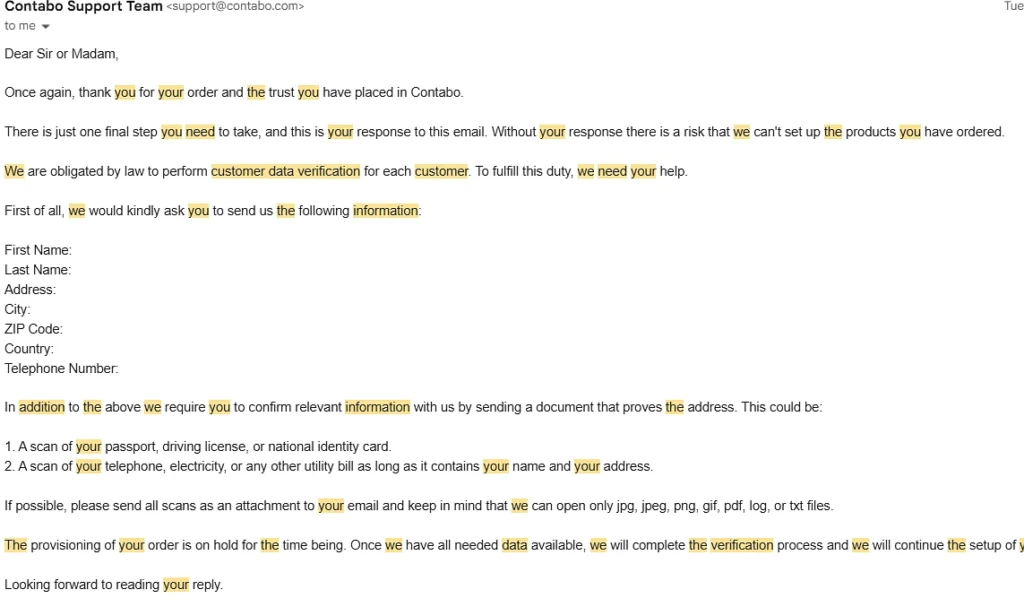
And then a second email arrives saying mandatory verification required, please send a scan of your passport or national identity card, plus a utility bill with your address on it, and by the way your server is on hold until you do.
But why ID needed now after payment and why I have to wait?
Already paid. They already have your card details. They already have your billing address, because the card wouldn’t have gone through if it didn’t match. And now they want a photo of your government ID before they’ll turn on a five dollar server.
Is this a bank account or a VPS?
What Law Exactly?
Contabo’s help page says it plainly. “We are obligated by law to perform customer data verification for each customer.” That’s the whole explanation. Obligated by law.
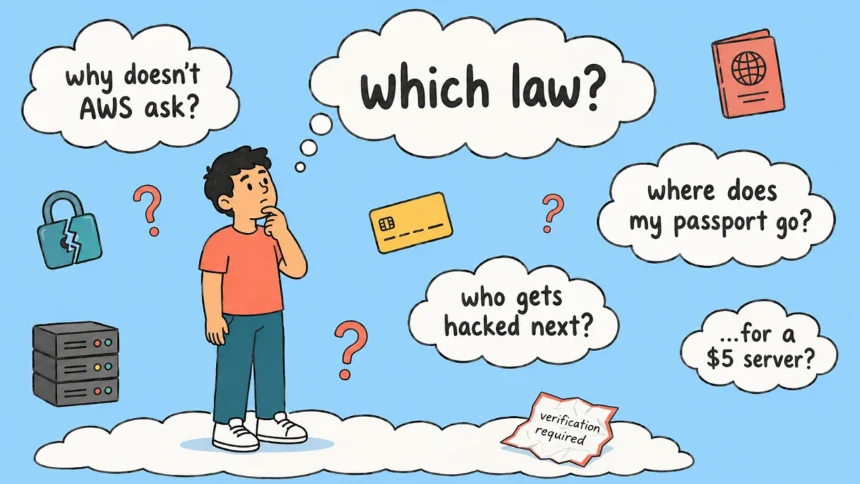
Which law though?
They don’t say. No statute named, no regulation number, no link to whatever legal framework supposedly requires a German company to collect passport scans from someone in Bangladesh, Egypt or India before switching on a virtual server.
Asking customers to email unredacted, unencrypted passport scans—and then storing those image files indefinitely on a helpdesk server—arguably violates the GDPR’s core principles of “data minimization” and “secure processing.”
Someone on LowEndTalk asked exactly this. “What law? I never heard about this law to ask copy of id from customers!” Nobody in that thread could name one either. And these are people who buy budget hosting constantly, they would know if such a law existed.
I really think this is just internal anti-fraud policy wearing a legal costume. Which is fine, companies can have policies. But say it’s your policy. Don’t tell me a law requires it when you can’t name the law.
Who gave them permission to hold your server hostage?
That’s the part that gets me. You already paid. The transaction completed. And then they hold what you bought until you hand over more personal documents than most banks ask for.
If a company wants ID verification, ask before the payment. Put it on the checkout page. “We require government ID verification before activation, expect 24 to 48 hours.” Then people can decide. Instead you find out after your money’s gone and you’re stuck waiting in a queue that moves whenever someone in their verification department feels like moving it.
Now the thing is $5/month budget host operates on razor-thin margins. If a fraudster uses a stolen credit card, the true cardholder initiates a chargeback.
If a company’s chargeback rate exceeds 1%, payment processors like Visa, Mastercard, or Stripe will financially penalize them or ban them entirely.
Now Let’s Talk About What Happens After You Send It
Say you comply. You email a scan of your passport, front and back, to a hosting company you found on Google twenty minutes ago.
Where does it go?
Which server does it sit on? Who inside the company can open it? Is it encrypted? How long do they keep it? What happens to it if they get acquired, or if they shut down, or if they get hacked?
And we have a solution for it (If both side of my ID are genuinely required, I don’t know if I bought a laptop/pc last time and i needed to show that):
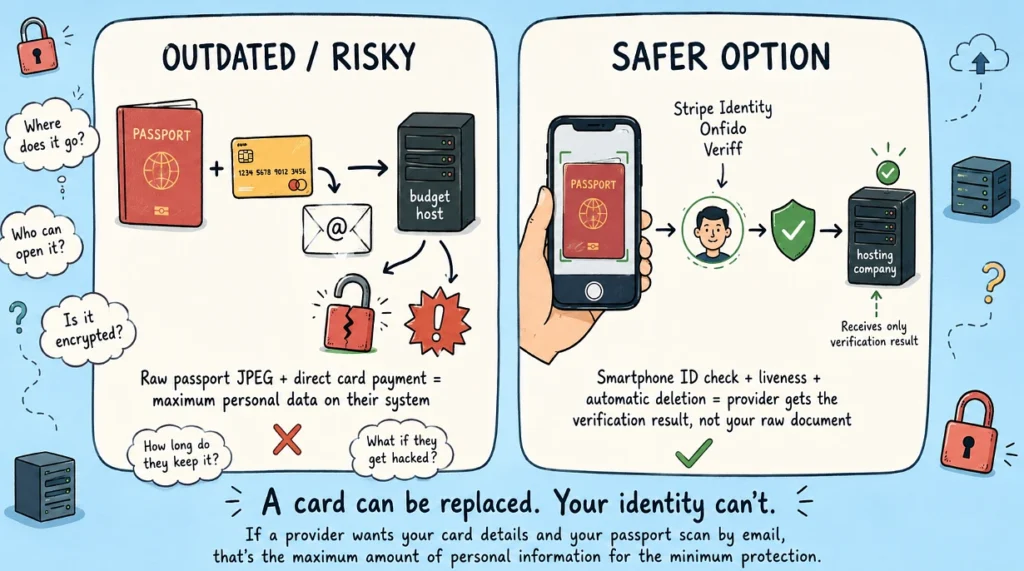
Modern services Stripe Identity, Onfido, or Veriff securely verify IDs using a smartphone camera, check biometric liveness to prevent Photoshop fakes, and then automatically delete the sensitive data so the company never actually holds the passport on its servers.
One important thing to note: Stripe can isolate verification data from the merchant’s own systems and lets businesses delete or redact it. But Stripe’s default policy retains non-biometric verification data for three years on behalf of the business, while biometric data may be retained for up to one year.
Budget hosts forcing users to send raw JPEGs via email are choosing the most outdated, insecure method possible.
And when they get hacked, who’s responsible?
Because hosting companies do get hacked. Epik, a domain registrar and hosting company, got breached in 2021 and 15 million unique email addresses leaked along with credit card information and internal company records. That’s a hosting company that collected customer data and then lost all of it.
And in 2026, Aura got breached 900,000 records. Names, addresses, phone numbers, emails. Aura sells identity theft protection. That’s their entire business. A company whose whole job is protecting your identity couldn’t protect its own customer list.
So now think about your passport scan sitting on some budget hosting provider’s server. If they get breached tomorrow, who’s responsible? They’ll send an apology email. Maybe offer credit monitoring for twelve months. And I wonder, if they lost my passport in that breach, did they lose my card details too? Probably yes, because the card is sitting in the same billing system.
A card you can replace in three days. Your passport number, your date of birth, your address, your photo, your signature, all of that is permanent. You can’t call your government and say please issue me a new identity because a hosting company got hacked.
So my honest question is this: isn’t it just better to go with a provider that doesn’t ask?
Obviously it is.
The Verification Loopholes Are Enormous
Here’s where the whole thing falls apart for me:
If someone uploads a fake ID, how would they even know?
They wouldn’t. That’s the answer.
These verification processes are manual. You email a scan. Someone looks at it. They check the name roughly matches the account. Done.
They are not running your passport number against any government database. They can’t. No hosting company has access to India’s passport system or Egypt’s national ID registry or Pakistan’s NADRA database. That access doesn’t exist for private companies.
So what are they actually verifying?
- A document exists — yes, you sent something that looks like an ID
- The name matches — roughly, if they squint
- The address matches your billing — if you filled it in correctly
That’s it. That’s the verification.
Someone could edit a scan in Photoshop. Someone could send a friend’s ID and sign up in that friend’s name. Someone could use a completely fabricated document that looks convincing enough. Any of that clears a manual review.
However, modern cybercriminals rarely bother with Photoshop. They simply buy pre-verified accounts.
The verification catches the laziest fraud, someone who typed a fake address and then can’t produce any document at all. Anyone putting even ten minutes of effort into it walks straight through.
Telegram channels are full of sellers offering “Aged & Verified Contabo/Hetzner Accounts.” The manual ID check stops the casual abuser, but organized cybercriminals bypass it entirely by using money mules or stolen identities to verify the accounts before reselling them.
So the legitimate customer sits waiting 48 hours with a charged card and no server. And the actual fraudster uploads a decent-looking fake and gets activated same day.
Is this really about my security or about their liability?
I think it’s liability. Plain and simple.
If someone uses their server for something illegal and police come asking, the company points to the passport scan and says look, we verified this customer, here’s the document on file. That protects the company.
It doesn’t protect you. Your protection would be them not having your passport at all.
Then Why Doesn’t AWS Ask?
This is the question I really want someone at these companies to answer.
Large platforms commonly combine payment verification, phone validation and automated risk scoring.
If ID verification is legally required for hosting providers, and if it’s genuinely about customer security, then explain why the biggest hosting companies in the world don’t do it.
- AWS — credit card, server running in minutes, no ID scan
- DigitalOcean — card or PayPal, server in under a minute, no ID scan
- Vultr — card, PayPal or crypto, server in minutes, no ID scan
- Linode — card, server in minutes, no ID scan
- Deltahost -card, even accepts Platon, Privat24, LiqPay, PayPal, no ID scan https://deltahost.com/
So either the law doesn’t exist, or AWS is breaking it every single day at enormous scale, or the law only applies to some providers for reasons nobody has explained.
And if it’s for customer safety, does AWS not care about customer safety?
That’s the logical follow-up. If collecting my passport makes me safer, then Deltahost.com is failing millions of customers by not collecting it. Vultr is putting people at risk. Linode doesn’t care about you.
Nobody actually believes that. Which means the safety argument doesn’t hold.
What AWS and DigitalOcean do instead is spend money on automated fraud detection. Card verification, 3D Secure, address matching, transaction scoring, behavioural analysis on signup patterns. If something looks wrong the system blocks it in real time. No human opens a passport scan. No customer waits two days.
AWS hosts infrastructure for governments, banks, hospitals. If a law required passport collection from hosting customers, AWS would be collecting passports. They’re not.
That costs money to build. A manual ID review process costs no such extra things. And that, I think, is the actual reason budget providers do it this way. It’s the cheap version of fraud prevention and the customer pays for it in privacy and waiting time.
Pay With PayPal Where You Can
One thing worth doing, and I say this to anyone signing up for hosting anywhere.
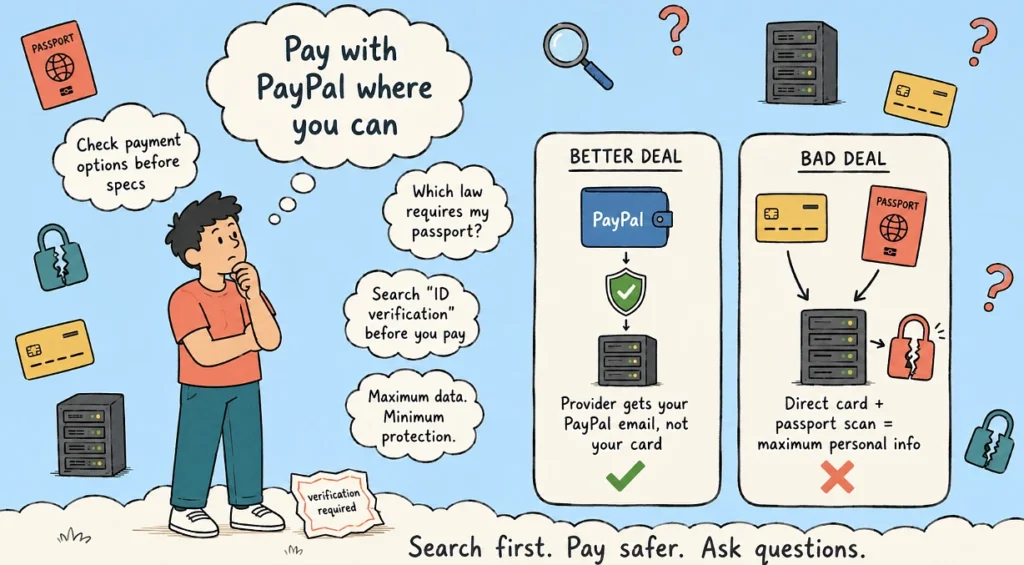
Check the payment options before you check the specs.
If a provider takes PayPal, use PayPal. Your card number never touches their system. PayPal handles the identity side on their end, and they’re actually built for that, it’s their entire business. If the hosting company gets breached later, they’ve got your PayPal email address or billing details.
Is PayPal perfect? No. But it’s better than emailing a passport scan to a company whose core competency is running servers, not securing identity documents.
The ones that only accept direct card payment and then also demand your passport on top of it are asking for the maximum amount of your personal information while giving you the minimum protection in return. That’s a bad deal and you should treat it like one.
Something worth keeping an eye on
If you’re signing up with a new provider, search their name plus “ID verification” before you pay. Check LowEndTalk, check Reddit, check their own help pages. Find out what they ask for before your card gets charged, not after.
And if a provider tells you a law requires your passport, ask them which law. See what they say.
I’d genuinely like to know the answer myself.